AI Memory Security Best Practices
AI Memory Security Best Practices
Secure persistent AI memory with scoped access, provenance, safe retrieval, and retention controls. Learn how to reduce memory-poisoning risks.
EverMind researchers
About 5 minutes to read

Persistent memory adds a security boundary: information written today may influence an agent in a later session. Malicious content can survive in stored records if write and retrieval controls allow it. Protect memory with scoped access, provenance, careful context assembly, and user-controlled correction and deletion. These controls complement model safety rather than replacing it.
Key Takeaways
• Persistent memory can carry injected instructions into later sessions, so memory writes and retrievals need their own security controls.
• Memory poisoning depends on the system’s write, retrieval, and instruction-handling behavior; storing a record does not give an attacker permanent or unlimited control.
• Treat retrieved memory as stored data, not as trusted instructions. Provenance helps assess a record but does not prove its content is safe.
• Combine access control, data minimization, retrieval safeguards, monitoring, and correction or deletion workflows.

What makes AI memory security different?
Persistent memory can extend the lifetime of a prompt-injection attempt. If a malicious instruction is stored and later retrieved, it may influence another interaction. The risk depends on whether the agent can write the content, retrieve it in a victim context, and mistake it for an instruction. Persistence creates an additional path to defend; it does not make every attack permanent.
OWASP’s prompt-injection guidance describes how untrusted content can manipulate model behavior. Memory adds another place that content may be encountered. Review stored conversation extracts, imported files, tool results, and agent-generated summaries as potential entry points rather than trusting them because they are already in a database.
Why does persistence change the threat model?
A poisoned record can outlive the original interaction and reappear when a related query retrieves it. Its impact depends on retention, scope, retrieval, and agent behavior. Deleting a record, repairing derived data, or blocking instruction-like content may limit that path; incident response must check the full memory lifecycle.
How does memory expand the attack surface?
Protect four practical surfaces: storage, retrieval, model interaction, and user control. Storage needs access boundaries and backups. Retrieval needs scope and provenance. Model interaction needs a clear distinction between evidence and instructions. Users and operators need ways to inspect, correct, and remove records.
How does agent context poisoning spread?
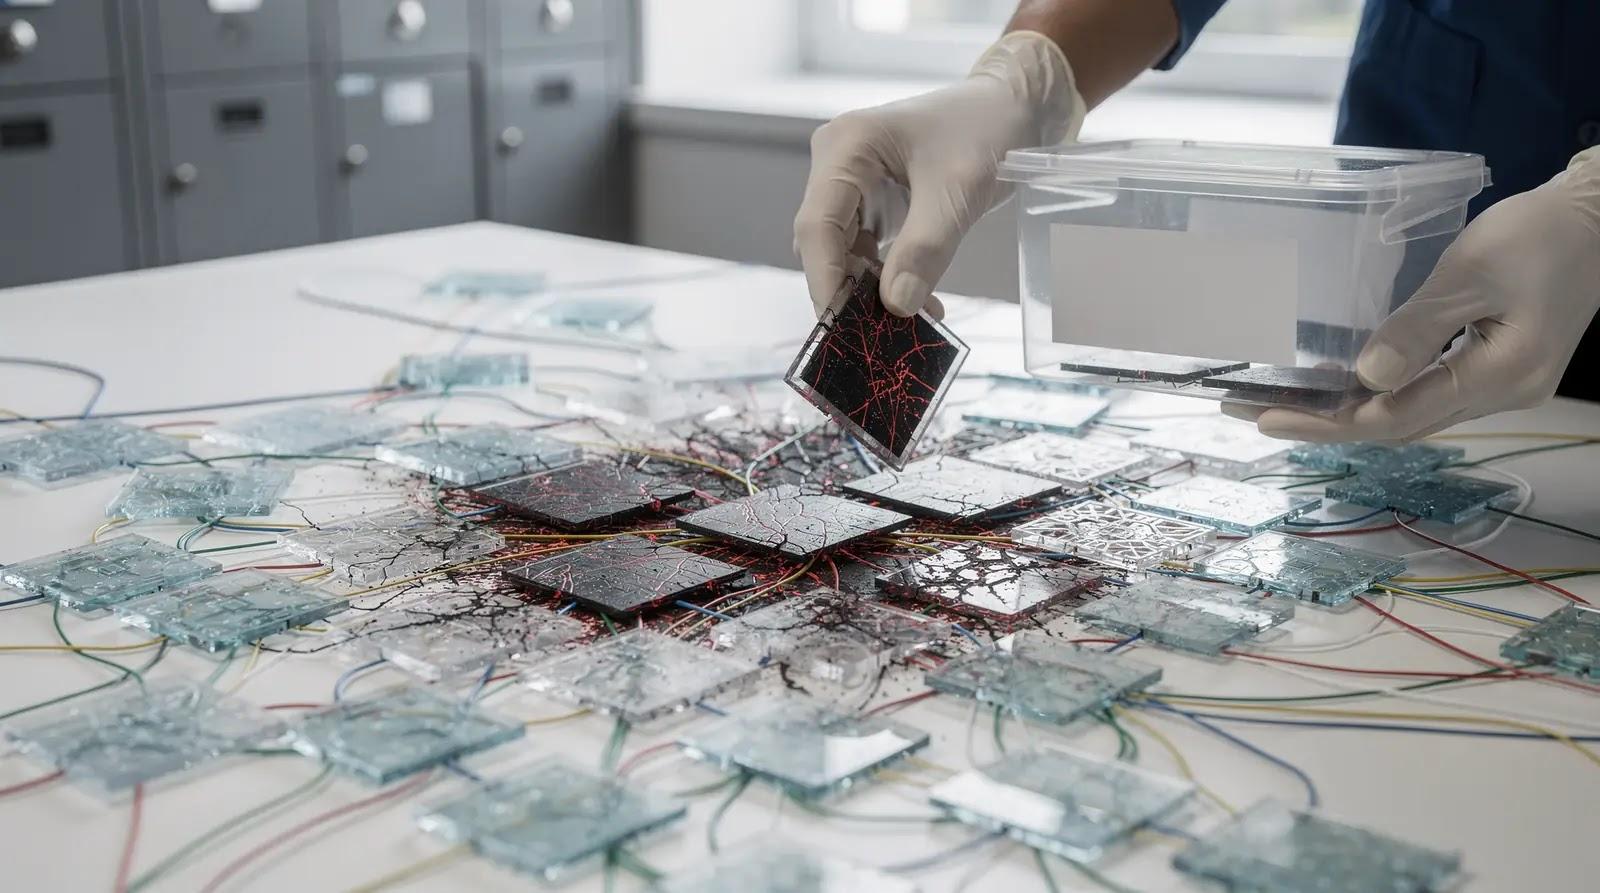
MINJA, by Dong and colleagues, studies query-only memory injection against evaluated memory-augmented agents. The attacker interacts through queries and observed outputs rather than directly editing the victim memory bank. The results demonstrate a possible attack path under the paper’s threat model—not that every memory system can be poisoned by any ordinary query.
The attacker’s goal is to get malicious records retained and later retrieved for a victim task. Separating sessions or users, constraining who can write to a shared scope, and treating remembered text as data can interrupt that chain. Test these controls together rather than relying on one filter.
How does memory poisoning relate to prompt injection?
Memory poisoning can carry prompt-injection content across time. A non-memory application can still persist malicious input in logs, files, or other systems, so session closure alone is not a universal security boundary. Track the sources that can become future model context.
How does agent context poisoning evade detection?
An attack may resemble normal conversation or a plausible task result, making it difficult to detect using request anomalies alone. Log memory mutations and relevant source information, monitor unusual cross-user writes or retrievals, and investigate changes that alter important instructions or operational facts.
What is a zero-trust memory architecture?
A zero-trust approach does not grant instruction authority to a record merely because it was stored earlier. Check who wrote it, which scope owns it, why it was retrieved, and whether using it is appropriate for the current task. Authentication, authorization, and content-handling controls address different parts of the problem.
Validate access scope before retrieval, preserve source and timestamp information, and keep recalled text separate from privileged instructions. Apply output and tool-use controls even when a memory looks legitimate. Provenance is useful evidence, not a complete defense against malicious or mistaken content.
How does zero-trust differ from perimeter security?
Perimeter controls protect entry points and network exposure. A zero-trust memory design also checks identity, authorization, and data handling within the system. These approaches complement each other; neither turns a stored memory into an inherently trustworthy instruction.
What layers require protection?
• Storage: use appropriate encryption, scoped access, tested backups, and retention limits.
• Retrieval: enforce user and project boundaries, and retain useful provenance.
• Model interaction: present recalled material as data and constrain sensitive tool actions.
• User control: provide inspection, correction, deletion, and auditable administrative actions.
EverMind’s EverOS stores durable memory as readable Markdown with local derived indexes. Its MCP connector documents a credential guard that refuses writes containing recognized secret formats, and it marks recalled memory as stored data rather than instructions. These are useful safeguards, not proof that all secrets or prompt injections will be detected. Use user, agent, app, project, and session identifiers deliberately; these scopes do not replace authentication and authorization. Protect self-hosted endpoints with appropriate access controls, review external model and embedding providers, and test deletion and recovery across source files and indexes (storage and processing; MCP security guidance).
FAQ
What makes AI memory security different from standard LLM security?
Persistent memory can retain harmful content that is retrieved in a later session. Protect the write-to-retrieval path and the agent’s use of that content; persistence alone does not guarantee a successful attack or indefinite control.
How does agent context poisoning spread through a memory system?
A vulnerable workflow may store content supplied through conversation, imports, or tool outputs, then retrieve it for a future task. MINJA demonstrates one query-only path in evaluated agents. Whether it works elsewhere depends on access scope, retention, retrieval, and instruction handling (research paper).
Why does persistent memory require defense-in-depth security?
Different controls cover different failure modes. Storage permissions cannot determine whether a sentence is a malicious instruction, and prompt filtering cannot replace user isolation or backups. Protect writes, reads, context assembly, and user-controlled correction together.
Conclusion
Build memory security around the complete data path: what is retained, who can retrieve it, how it enters the prompt, and how it can be corrected or deleted. Readable storage and provenance make investigation easier, while scoped access and cautious instruction handling reduce opportunities for abuse. Re-test those boundaries as agents, providers, and retention policies change.
Persistent memory adds a security boundary: information written today may influence an agent in a later session. Malicious content can survive in stored records if write and retrieval controls allow it. Protect memory with scoped access, provenance, careful context assembly, and user-controlled correction and deletion. These controls complement model safety rather than replacing it.
Key Takeaways
• Persistent memory can carry injected instructions into later sessions, so memory writes and retrievals need their own security controls.
• Memory poisoning depends on the system’s write, retrieval, and instruction-handling behavior; storing a record does not give an attacker permanent or unlimited control.
• Treat retrieved memory as stored data, not as trusted instructions. Provenance helps assess a record but does not prove its content is safe.
• Combine access control, data minimization, retrieval safeguards, monitoring, and correction or deletion workflows.
What makes AI memory security different?
Persistent memory can extend the lifetime of a prompt-injection attempt. If a malicious instruction is stored and later retrieved, it may influence another interaction. The risk depends on whether the agent can write the content, retrieve it in a victim context, and mistake it for an instruction. Persistence creates an additional path to defend; it does not make every attack permanent.
OWASP’s prompt-injection guidance describes how untrusted content can manipulate model behavior. Memory adds another place that content may be encountered. Review stored conversation extracts, imported files, tool results, and agent-generated summaries as potential entry points rather than trusting them because they are already in a database.
Why does persistence change the threat model?
A poisoned record can outlive the original interaction and reappear when a related query retrieves it. Its impact depends on retention, scope, retrieval, and agent behavior. Deleting a record, repairing derived data, or blocking instruction-like content may limit that path; incident response must check the full memory lifecycle.
How does memory expand the attack surface?
Protect four practical surfaces: storage, retrieval, model interaction, and user control. Storage needs access boundaries and backups. Retrieval needs scope and provenance. Model interaction needs a clear distinction between evidence and instructions. Users and operators need ways to inspect, correct, and remove records.
How does agent context poisoning spread?
MINJA, by Dong and colleagues, studies query-only memory injection against evaluated memory-augmented agents. The attacker interacts through queries and observed outputs rather than directly editing the victim memory bank. The results demonstrate a possible attack path under the paper’s threat model—not that every memory system can be poisoned by any ordinary query.
The attacker’s goal is to get malicious records retained and later retrieved for a victim task. Separating sessions or users, constraining who can write to a shared scope, and treating remembered text as data can interrupt that chain. Test these controls together rather than relying on one filter.
How does memory poisoning relate to prompt injection?
Memory poisoning can carry prompt-injection content across time. A non-memory application can still persist malicious input in logs, files, or other systems, so session closure alone is not a universal security boundary. Track the sources that can become future model context.
How does agent context poisoning evade detection?
An attack may resemble normal conversation or a plausible task result, making it difficult to detect using request anomalies alone. Log memory mutations and relevant source information, monitor unusual cross-user writes or retrievals, and investigate changes that alter important instructions or operational facts.
What is a zero-trust memory architecture?
A zero-trust approach does not grant instruction authority to a record merely because it was stored earlier. Check who wrote it, which scope owns it, why it was retrieved, and whether using it is appropriate for the current task. Authentication, authorization, and content-handling controls address different parts of the problem.
Validate access scope before retrieval, preserve source and timestamp information, and keep recalled text separate from privileged instructions. Apply output and tool-use controls even when a memory looks legitimate. Provenance is useful evidence, not a complete defense against malicious or mistaken content.
How does zero-trust differ from perimeter security?
Perimeter controls protect entry points and network exposure. A zero-trust memory design also checks identity, authorization, and data handling within the system. These approaches complement each other; neither turns a stored memory into an inherently trustworthy instruction.
What layers require protection?
• Storage: use appropriate encryption, scoped access, tested backups, and retention limits.
• Retrieval: enforce user and project boundaries, and retain useful provenance.
• Model interaction: present recalled material as data and constrain sensitive tool actions.
• User control: provide inspection, correction, deletion, and auditable administrative actions.
EverMind’s EverOS stores durable memory as readable Markdown with local derived indexes. Its MCP connector documents a credential guard that refuses writes containing recognized secret formats, and it marks recalled memory as stored data rather than instructions. These are useful safeguards, not proof that all secrets or prompt injections will be detected. Use user, agent, app, project, and session identifiers deliberately; these scopes do not replace authentication and authorization. Protect self-hosted endpoints with appropriate access controls, review external model and embedding providers, and test deletion and recovery across source files and indexes (storage and processing; MCP security guidance).
FAQ
What makes AI memory security different from standard LLM security?
Persistent memory can retain harmful content that is retrieved in a later session. Protect the write-to-retrieval path and the agent’s use of that content; persistence alone does not guarantee a successful attack or indefinite control.
How does agent context poisoning spread through a memory system?
A vulnerable workflow may store content supplied through conversation, imports, or tool outputs, then retrieve it for a future task. MINJA demonstrates one query-only path in evaluated agents. Whether it works elsewhere depends on access scope, retention, retrieval, and instruction handling (research paper).
Why does persistent memory require defense-in-depth security?
Different controls cover different failure modes. Storage permissions cannot determine whether a sentence is a malicious instruction, and prompt filtering cannot replace user isolation or backups. Protect writes, reads, context assembly, and user-controlled correction together.
Conclusion
Build memory security around the complete data path: what is retained, who can retrieve it, how it enters the prompt, and how it can be corrected or deleted. Readable storage and provenance make investigation easier, while scoped access and cautious instruction handling reduce opportunities for abuse. Re-test those boundaries as agents, providers, and retention policies change.
You may also like these
Related

Multi-round retrieval: letting the model decide when to stop searching
multi-round retrieval,agentic retrieval,fixed top-k,injection budget,core selection,EverOS,agent memory,LoCoMo,LongMemEval,EverMemBench,SubtleMemory,multi-hop retrieval,retrieval accuracy,prompt token cost

Do public SKILL.md files actually make agents better?
SkillCorpus,SKILL.md,agent skills,skill curation,skill retrieval,LLM agents,SkillsBench,GDPVal,agent harness

CRAFT: learning how to fuse video tokens, not just which to drop
CRAFT,video token compression,vision-language models,video VLM,KV cache,prefill cost,token merging,token pruning,temporal reasoning

Self-evolving agents have a measurement problem
self-evolving agents,agent harness,HarnessBank,credit assignment,LLM agents,agent evaluation,harness optimization,significance testing
AI Memory Security Best Practices
Secure persistent AI memory with scoped access, provenance, safe retrieval, and retention controls. Learn how to reduce memory-poisoning risks.
EverMind researchers
About 5 minutes to read
EverMind
A straightforward solution to long-term coherence
Scan to join the community

Discord

© 2026 EverMind Team.
EverMind
A straightforward solution to long-term coherence
Scan to join the community
Discord
© 2026 EverMind Team.
EverMind
A straightforward solution to long-term coherence
Scan to join the community
Discord
© 2026 EverMind Team.